How do you make a complex Java application SBOM-ready for the EU Cyber Resilience Act?
In this, Ixchel Ruiz and Markus Schlichting provide a clear and technical overview of what Java engineers, architects and DevOps teams must understand in order to meet CRA expectations and to avoid risk under NIS2 and DORA. These two initiatives increasingly treat SBOMs as evidence of supply-chain control.
The session covers practical challenges in Java software supply chains, including:
- transitive dependencies
- shaded JAR contents
- BOM-managed versions
- container layers
- embedded services and runtime components
- SBOM generation with Maven, Gradle and CycloneDX
- container-image inventories
- Dependency-Track for vulnerability and license visibility
- workflows and governance for keeping SBOMs accurate across releases
The goal: make software systems SBOM-ready while improving software quality and supply-chain resilience.
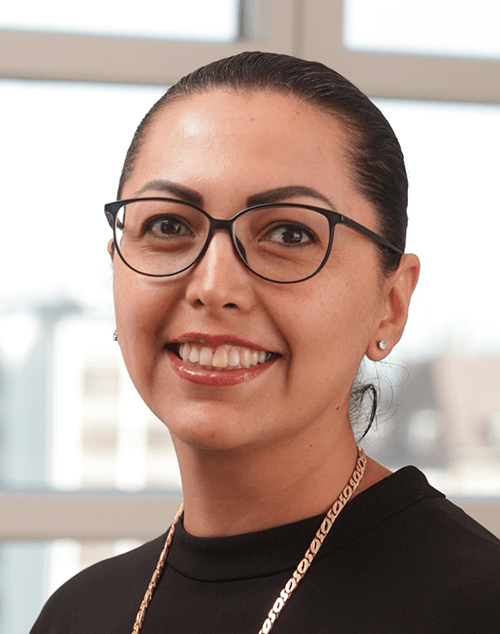 Ix-chel Ruiz has developed software application & tools since 2000. Her research interests include Java, dynamic languages, client-side technologies and testing. Java Champion, Oracle ACE pro, Testcontainers Community Champion, CDF Ambassador, Hackergarten enthusiast, Open Source advocate, public speaker and mentor.
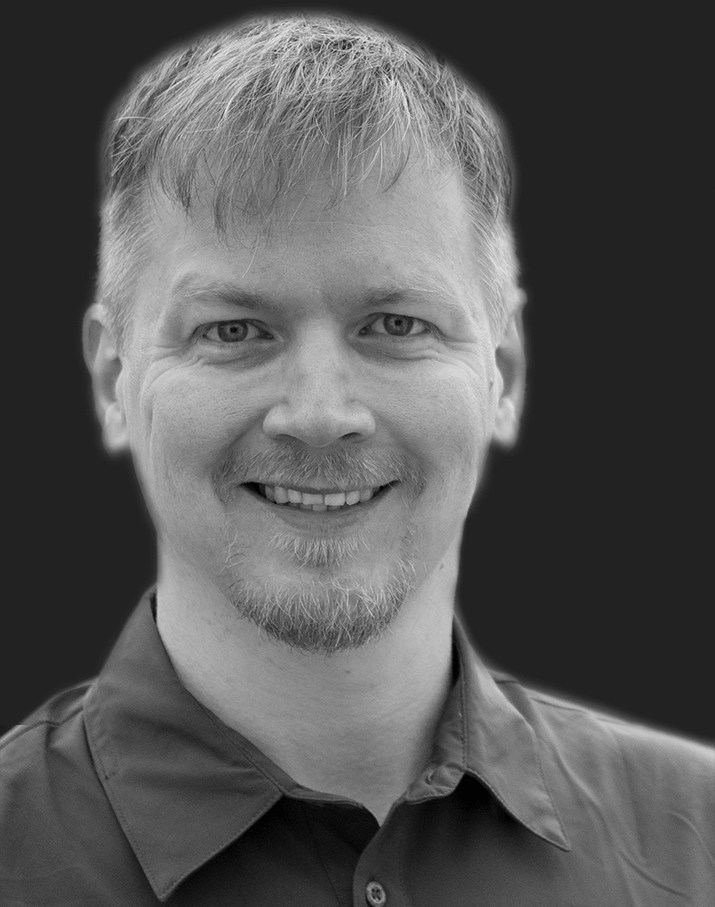 Markus Schlichting is a co-founder of Karakun AG and lives in Siegburg, Germany. He is organizer of the Hackergarten in Basel and occasionally speaks at user groups and conferences and writes articles. Software Engineering, agile methodology and Open Source are concerns of his heart.
When not sitting in front of a computer, he loves to spend time with his sons and his wife, taking photographs or to get some fresh air driving his motorbike.